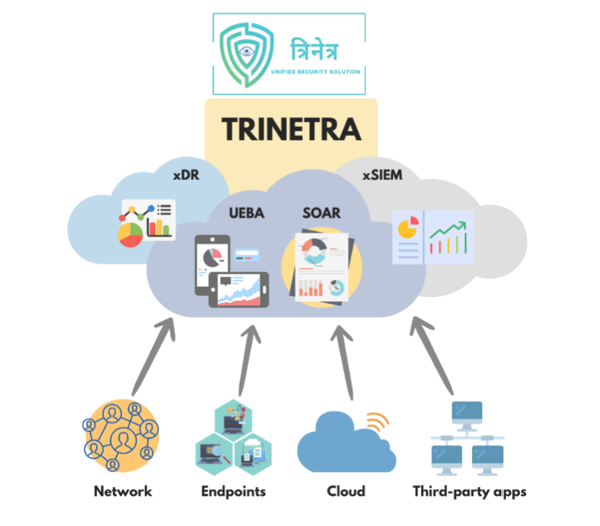
TRINETRA ENTERPRISE is an indigenous, unified AI-Powered Cyber Resilience platform for enterprise security developed by the Centre for Development of Telematics (C-DOT), Government of India. It was created to address a persistent fragmentation in enterprise security - important controls are frequently distributed across separate products, consoles and operating teams. This can delay correlation, create visibility gaps and increase the effort required to investigate, contain and report incidents. TRINETRA is positioned as the only platform engineered as one fabric with all the tools plus threat intelligence.
Most organizations end up with multiple security tools, each with their own agent, dashboard and license. TRINETRA replaces that patchwork with single lightweight agent and unified platform. It covers endpoint management, threat detection and response, log analysis, automated response, user behaviour analytics, data loss prevention, and audit and compliance reporting.
It aims to bridge the gaps in current cybersecurity approaches by integrating functionalities of various security product verticals including Endpoint Detection and Response (EDR), Security Information and Event Management (SIEM), Security Orchestration and Automated Response (SOAR), User and Entity Behavior Analytics (UEBA), Unified Endpoint Management (UEM), Data Loss Prevention (DLP), Security Audit Benchmark and Compliance (SABC) into a unified, proactive security framework.
You don’t have to buy everything at once. Start with one module or take the full suite, and run it on premises, on the cloud or as a hybrid. If you don’t have your own security team, C-DOT’s partners can run a 24x7 SOC for you. Because it’s built and supported in India, your data stays in India.
View Product Video
• 24x7 monitoring: Keeps watch on your IT assets and network traffic around the clock and flags suspicious activity.
• Detection without signatures: Behavioural AI catches new and unknown threats, including ransomware, fileless attacks and zero-day exploits.
• Automatic blocking: Stops unauthorised access, malicious activity and data leaks by default.
• Quick containment: Isolates compromised devices, quarantines files and rolls back ransomware changes in seconds. Anything destructive needs a human’s approval first.
• Insider threat detection: Learns how each user normally behaves and raises an alert when something looks off, such as a login from an impossible location.
• Ready-made response playbooks: Over 120 code-free playbooks handle common incidents like credential abuse, phishing and ransomware.
• Threat intelligence: Combines C-DOT’s own intelligence, and global sources.
• Always-on audits and compliance: Regularly checks systems for vulnerabilities and misconfigurations, and produces audit-ready reports mapped to CIS, NIST CSF 2.0, ISO 27001 and DPDP.
• Data protection: Classifies sensitive data, controls USB and other devices, and prevents data from leaving your network.
• Comprehensive Coverage: Endpoint, network, cloud and data protection with built in audit and compliance support.
• Single Lightweight Agent: Delivers UEM, EDR and DLP with minimal impact (under 80 MB RAM and under 2% CPU per endpoint).
• Broad endpoint support: Desktops, laptops, virtual machines and servers.
• Rapid Detection: Sub second behavioural alerts to contain threats early.
• Enterprise Scale Data: Ingests 1 million+ events per second with 100+ prebuilt parsers and 200+ native connectors.
• Strong Threat Coverage: Mapped to MITRE ATT&CK with 1,500+ correlation rules, updated weekly.
• Built in Automation: 120+ ready to use SOAR playbooks to speed response.
• Compliance Ready: Supports CIS Benchmarks, NIST CSF 2.0, ISO 27001, RBI guidelines and DPDP.
• Single Pane of Glass: Unified console and a unified security data lake for logs, telemetry and threat intelligence.
TRINETRA is built for organisations that can’t afford to compromise on security or data control, including:
• Government departments and ministries that need state-wide or nation-wide visibility while local offices keep control of their own systems.
• Banking and financial services, for ransomware protection, insider-threat detection and certification compliance.
• Telecom operators, for protecting large networks, workforces and subscriber data.
• Law enforcement and public safety, for protecting sensitive records and keeping digital evidence intact.
• Energy, PSUs and critical infrastructure, including railways, with support for OT and SCADA environments.
• Defence and strategic sectors, with support for classified and air-gapped networks.
• Academic institutions and healthcare, for protecting research, student and patient data.
Awards and Recognitions
• Digital Transformation Award 2026
• ET Government DigiTech Award 2025
• ET Telecom Award 2025
• Golden Peacock Innovative Product/Service Award 2025
• Bharat Cyber Suraksha Award 2025
• Cybersecurity Excellence in Governance 2025
• Technology Sabha Awards 2024 (Express Computer), Enterprise Security category
• Named among the Top 50 Leading Organisations in Cybersecurity by Alden Global
Government & strategic agencies in BFSI, Law & Enforcement Agencies, State Police, Telecom, PSUs and Natural Gas sectors.
Certifications and test results
• 100% detection in AV-Lab Cybersecurity Foundation’s Advanced In-The-Wild Malware Test (January 2026), rated "Excellent"
• ISO/IEC 27001:2022 certified for information security management
• 24x7 monitoring: Keeps watch on your IT assets and network traffic around the clock and flags suspicious activity.
• Detection without signatures: Behavioural AI catches new and unknown threats, including ransomware, fileless attacks and zero-day exploits.
• Automatic blocking: Stops unauthorised access, malicious activity and data leaks by default.
• Quick containment: Isolates compromised devices, quarantines files and rolls back ransomware changes in seconds. Anything destructive needs a human’s approval first.
• Insider threat detection: Learns how each user normally behaves and raises an alert when something looks off, such as a login from an impossible location.
• Ready-made response playbooks: Over 120 code-free playbooks handle common incidents like credential abuse, phishing and ransomware.
• Threat intelligence: Combines C-DOT’s own intelligence, and global sources.
• Always-on audits and compliance: Regularly checks systems for vulnerabilities and misconfigurations, and produces audit-ready reports mapped to CIS, NIST CSF 2.0, ISO 27001 and DPDP.
• Data protection: Classifies sensitive data, controls USB and other devices, and prevents data from leaving your network.
• Comprehensive Coverage: Endpoint, network, cloud and data protection with built in audit and compliance support.
• Single Lightweight Agent: Delivers UEM, EDR and DLP with minimal impact (under 80 MB RAM and under 2% CPU per endpoint).
• Broad endpoint support: Desktops, laptops, virtual machines and servers.
• Rapid Detection: Sub second behavioural alerts to contain threats early.
• Enterprise Scale Data: Ingests 1 million+ events per second with 100+ prebuilt parsers and 200+ native connectors.
• Strong Threat Coverage: Mapped to MITRE ATT&CK with 1,500+ correlation rules, updated weekly.
• Built in Automation: 120+ ready to use SOAR playbooks to speed response.
• Compliance Ready: Supports CIS Benchmarks, NIST CSF 2.0, ISO 27001, RBI guidelines and DPDP.
• Single Pane of Glass: Unified console and a unified security data lake for logs, telemetry and threat intelligence.
TRINETRA is built for organisations that can’t afford to compromise on security or data control, including:
• Government departments and ministries that need state-wide or nation-wide visibility while local offices keep control of their own systems.
• Banking and financial services, for ransomware protection, insider-threat detection and certification compliance.
• Telecom operators, for protecting large networks, workforces and subscriber data.
• Law enforcement and public safety, for protecting sensitive records and keeping digital evidence intact.
• Energy, PSUs and critical infrastructure, including railways, with support for OT and SCADA environments.
• Defence and strategic sectors, with support for classified and air-gapped networks.
• Academic institutions and healthcare, for protecting research, student and patient data.
Awards and Recognitions
• Digital Transformation Award 2026
• ET Government DigiTech Award 2025
• ET Telecom Award 2025
• Golden Peacock Innovative Product/Service Award 2025
• Bharat Cyber Suraksha Award 2025
• Cybersecurity Excellence in Governance 2025
• Technology Sabha Awards 2024 (Express Computer), Enterprise Security category
• Named among the Top 50 Leading Organisations in Cybersecurity by Alden Global
Government & strategic agencies in BFSI, Law & Enforcement Agencies, State Police, Telecom, PSUs and Natural Gas sectors.